Audience
Industrial, infrastructure, utilities, and critical-operations teams responsible for OT/ICS risk and resilience.
Critical Infrastructure · Application portfolio
An operating picture for OT/ICS risk - asset criticality, controls, network exposure, and business impact in one governed view.
Audience
Industrial, infrastructure, utilities, and critical-operations teams responsible for OT/ICS risk and resilience.
Question
Which OT risk deserves action first when operational consequence is included?
Output
A prioritized risk and resilience view with affected assets, processes, response options, and the evidence needed for the OT owner to approve next steps.
Decision logic
Operational criticality, exposure, control dependency, maintenance windows, compensating controls, and business impact can be modeled together so remediation is ranked by consequence rather than by vulnerability lists alone.
Integration requirements
Action authority
OT, cyber, operations, and compliance leaders define action boundaries; control-system and safety-system changes stay under the established operational authority.
A concrete decision workflow
Step 1
Which OT risk deserves action first when operational consequence is included?
Step 2
OT/ICS asset inventories · SCADA & historians · Network and segmentation data · Maintenance systems · Vulnerability data · OT/ICS telemetry and control-system state · Fixed camera and sensor coverage across regulated areas
Step 3
Operational criticality, exposure, control dependency, maintenance windows, compensating controls, and business impact can be modeled together so remediation is ranked by consequence rather than by vulnerability lists alone.
Step 4
A prioritized risk and resilience view with affected assets, processes, response options, and the evidence needed for the OT owner to approve next steps. OT, cyber, operations, and compliance leaders define action boundaries; control-system and safety-system changes stay under the established operational authority.
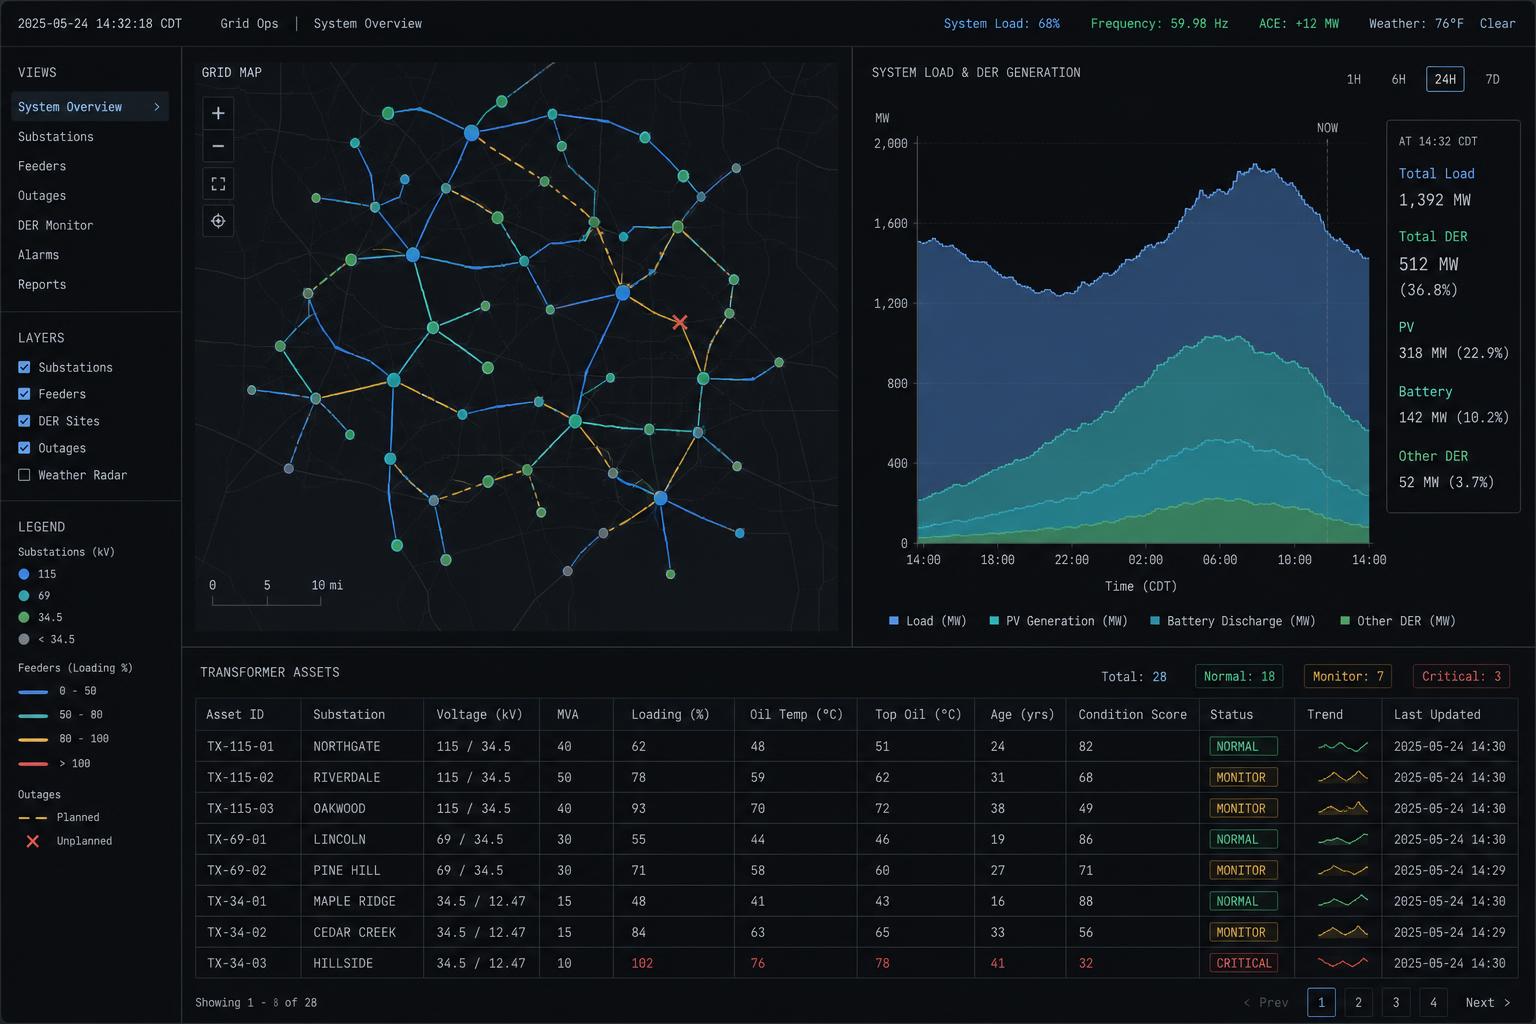
Representative interface · Product status not independently verified · Not a customer deployment
Source context, recommendations, permissions, and operator review remain visible on the same working surface.
The path begins with one bounded decision, connects the systems holding its evidence, puts a working surface in front of operators, then hardens permissions and audit before expanding.
Public customer case studies are not yet available. The workflows shown here are representative and are not customer attributions or performance claims.
One operating view · OT Risk & Resilience Center
The same working path runs through every Ridgeline application.